AI compliance automation turns regulatory text and system telemetry into continuous, audit-ready evidence and enforceable policy checks. It maps obligations under frameworks the NIST cyber framework profiles and the EU AI Act define, converts them into machine-readable controls, and monitors production systems for drift. This capability is built as owned infrastructure rather than a rented dashboard, which changes how the rest of this guide should be read: as an architecture decision, not a tool purchase.
TL;DR:
- Cross-framework mapping enables organizations to reuse controls across multiple regulations, reducing redundant evidence collection and audit effort.
- Effective implementation starts by focusing on one system and one framework during pilot phases, avoiding project stalls caused by scope creep.
- Continuous monitoring and real-time drift detection replace traditional point-in-time audits, providing proactive compliance insights and early issue discovery.
- AI models are prone to misclassification and require human review gates for high-stakes findings, especially under shifting regulations like the EU AI Act.
- Building an AI-native, self-hosted compliance stack offers greater control over data, models, and audit trails, supporting scalable regulatory management.
Table of Contents
- How AI Compliance Automation Works: Architecture and Data Flow
- What Are the Core Capabilities of Compliance Automation?
- How Do You Implement Compliance Automation Step by Step?
- Why Cross-Framework Mapping Saves the Most Time
- Who Should Own AI Compliance Governance?
- Where Does AI Compliance Automation Deliver the Fastest Results?
- What Are the Risks and Limits of AI Compliance Automation?
- Why Owning the Compliance Stack Beats Renting It
- Build Your Compliance Stack Instead of Renting One
- Standards Worth Reviewing Before You Build
- Sources
- FAQ
How AI Compliance Automation Works: Architecture and Data Flow
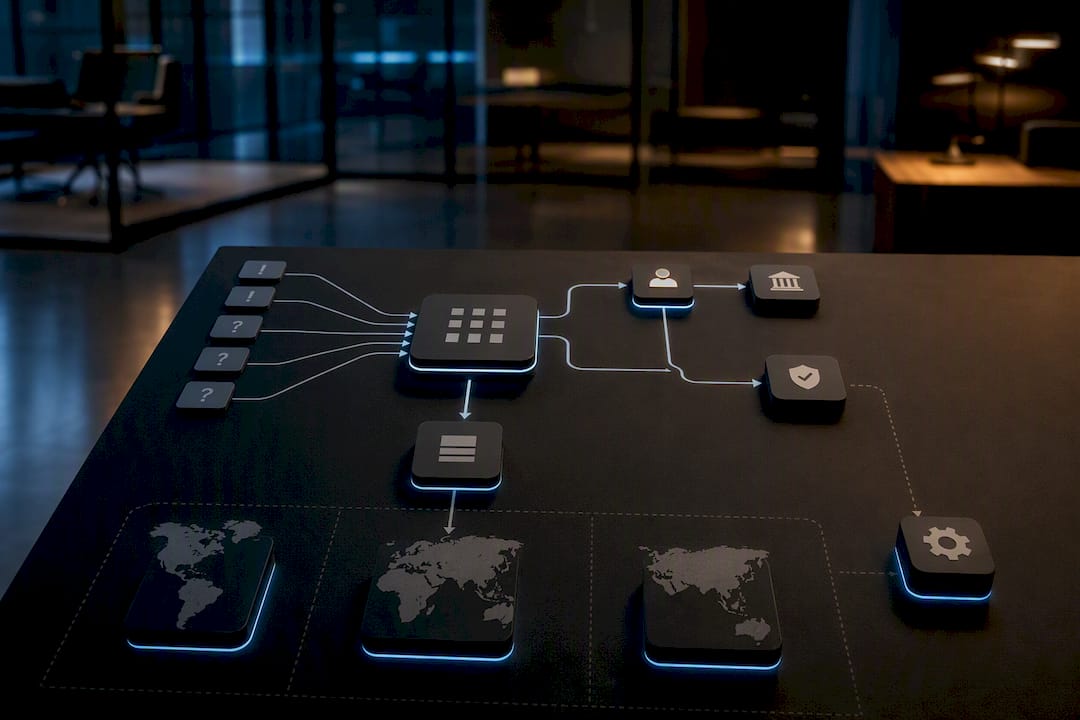
Every automated compliance system runs on three layers: inputs, processing, and outputs. Understanding where each layer sits determines whether a rollout takes three months or eighteen.
Inputs come from two very different worlds. Regulatory feeds, statutory text, and agency guidance provide the “what must be true” side. Logs, code repositories, cloud telemetry, and identity provider events provide the “what is actually happening” side. The system’s entire value comes from reconciling those two streams continuously instead of quarterly.
Processing happens in layers that specialize:
- Natural language processing models extract discrete obligations from regulatory text and convert vague legal language into testable statements.
- Machine learning risk scoring ranks which gaps matter most, based on exposure, data sensitivity, and historical incident patterns.
- Policy-as-code engines translate approved controls into scripts that run automatically against infrastructure.
- Connectors pull evidence from cloud platforms, identity systems, and version control without manual export.
Outputs are what auditors and regulators actually see: structured audit trails, technical dossiers mapped to specific control IDs, automatically generated policies, and alerts routed to the right owner when something drifts out of compliance. OSCAL, NIST’s machine-readable control format, is increasingly the backbone for this layer because it lets a single control definition feed multiple downstream systems without manual reformatting.
Integration touchpoints matter more than most vendors admit upfront. A system that cannot hook into your CI/CD pipeline, your SIEM, your identity provider (Okta, Azure AD, or similar), and your primary cloud platform will generate reports nobody trusts, because the underlying data is stale the moment it is pulled.
What Are the Core Capabilities of Compliance Automation?
Four capabilities do almost all the work in a mature deployment, and each one produces a distinct, checkable output.
- Horizon scanning. The system watches regulatory feeds and flags new or amended obligations before they become enforcement risk. Success looks like a two-week head start on a rule change, not a scramble after a fine.
- Obligation extraction. NLP models parse statutory or standard text and convert it into structured, testable statements, essentially turning a 40-page regulation into a checklist a machine can verify. This is where legal review still matters most: extraction proposes, a human confirms.
- Evidence collection. Connectors pull configuration states, access logs, and change records automatically, then apply confidence scoring so reviewers know which evidence is solid and which needs a second look.
- Continuous monitoring and drift detection. Instead of a point-in-time audit, the system re-checks controls on every deploy or on a fixed interval, catching a misconfigured permission or an expired certificate before it becomes a finding.
The Cloud Security Alliance’s assessment of compliance automation frames this shift plainly: proactive, continuous evidence trails are replacing the old point-in-time audit model, and organizations that haven’t made the shift are increasingly the ones facing surprise findings.
Pro Tip: Start obligation extraction with one framework you know cold, not the most complex one you own. A team that first tests extraction accuracy against a framework they already understand catches modeling errors fast, before those errors propagate into unfamiliar territory like the EU AI Act.
How Do You Implement Compliance Automation Step by Step?
Rollout succeeds or fails on scoping discipline, not on model sophistication. Start narrow.
Begin with an inventory: which systems hold regulated data, which frameworks apply to each, and which control gaps carry the highest exposure. Pick one system and one framework for the pilot. Trying to automate five frameworks across a full environment in phase one is the single most common reason these projects stall.
Policy-as-code is the technical backbone of enforcement. Teams write validation scripts that check specific controls, wire them into CI/CD as pre-deploy hooks, and let the pipeline block a release that fails a check rather than flagging it after the fact. A practitioner-level pattern worth borrowing: policy-as-code checks catch missing controls before deployment, which is far cheaper than catching them in a post-incident review.
Evidence pipelines need the same rigor as the controls themselves:
- Define exactly what gets extracted (config snapshots, access changes, deployment records).
- Store evidence with immutable timestamps and clear chain-of-custody metadata.
- Route low-confidence evidence to human reviewers automatically rather than silently accepting it.
A typical phased timeline runs pilot (60 to 90 days, one framework, one system), scale (add frameworks and systems over two to three quarters), then operate (steady-state monitoring with quarterly governance reviews). Compliance owns the control definitions; engineering owns the CI/CD hooks; security owns evidence storage.
Why Cross-Framework Mapping Saves the Most Time
Most regulated organizations answer to more than one framework, and most controls overlap heavily across them. Cross-framework mapping means defining a control once and tagging it against every framework it satisfies, instead of building separate evidence for SOC 2, ISO 27001, NIST, and the EU AI Act every time an auditor asks.
The FINOS Common Cloud Controls Project is a useful reference point here: it publishes reusable control definitions specifically designed to standardize cloud implementations so teams stop rebuilding the same evidence under different names.
Good mapping practice looks like this:
- Design evidence collection around the control’s underlying intent, not the specific wording of one framework.
- Maintain a mapping table that ties each internal control ID to every external framework requirement it covers.
- Review mappings quarterly, since framework updates (especially around AI-specific rules) shift faster than most internal review cycles.
Mapping has real limits. Jurisdictional requirements sometimes demand separate evidence by law, and a control that satisfies ISO 27001’s access management clause may not fully satisfy a stricter sector-specific rule. Treat mapping as a time-saver, not a substitute for legal judgment on where overlap genuinely ends.
Who Should Own AI Compliance Governance?
Automation without ownership clarity creates its own risk. A basic RACI split works for most organizations: compliance is accountable for control definitions, engineering is responsible for implementation, security owns evidence integrity, and legal consults on interpretation of new obligations.
- Set human review triggers explicitly. Any control failure touching customer data, financial reporting, or a regulated AI model output should route to a named reviewer, not sit in a queue.
- Define escalation paths before you need them. A drift alert on a low-risk system can wait a day; one on a payment system cannot.
- Produce regulator-ready artifacts continuously, not just before an audit window, so auditor access requests take hours instead of weeks.
- Run a quarterly governance review that checks whether mappings, thresholds, and escalation rules still match current regulatory text.
Pro Tip: Give auditors a read-only view into the live evidence system instead of a static export. It cuts audit prep time dramatically because auditors stop waiting on your team to compile what the system already has.
Where Does AI Compliance Automation Deliver the Fastest Results?
Impact varies sharply by industry, and the fastest wins tend to come from the most evidence-heavy processes.
- Finance: Automating transaction monitoring evidence and access control reviews for frameworks like SOX cuts the manual evidence-gathering burden that usually eats weeks before an audit.
- Healthcare: Continuous monitoring against frameworks like 21 CFR Part 11 helps regulated life sciences teams keep electronic records and signatures audit-ready without a manual quarterly sweep.
- Enterprise SaaS: Mapping SOC 2 and ISO 27001 controls once and reusing evidence across both frameworks removes duplicate work during renewal cycles.
Common blockers across all three: legacy systems without API access, and compliance teams that were never looped into the initial connector scoping.
What Are the Risks and Limits of AI Compliance Automation?
Models still misclassify obligations and produce false positives, especially with ambiguous regulatory language. Explainability gaps make some automated decisions hard to defend to a regulator without a human translating the logic. The EU AI Act’s phased enforcement timeline and shifting state-level rules in the US mean mappings need real maintenance, not a one-time setup. Data sovereignty rules can also affect whether automated evidence is even admissible in some jurisdictions. Mitigate all of this with mandatory human review gates on high-stakes findings, conservative default enforcement (block first, allow after review), and logging thorough enough to reconstruct any automated decision after the fact.
Why Owning the Compliance Stack Beats Renting It
Renting compliance tools means renting someone else’s roadmap, someone else’s data residency choices, and someone else’s uptime. AI-native compliance systems with self-hosted large language models and embedded engineering teams enable regulated firms to keep their evidence, models, and audit trail entirely under their own control. That ownership model lets a firm scale tenfold without scaling headcount at the same rate, making an audit trail defensible instead of just convenient.
— Matevz
Build Your Compliance Stack Instead of Renting One
Most compliance automation vendors sell you a dashboard and keep the underlying model, the data pipeline, and the roadmap. This approach offers a compliance-first AI system your team owns outright, deployed with self-hosted models so regulated data never leaves your infrastructure.
A first conversation typically covers three things: which frameworks and systems you need automated first, what your current evidence gaps actually cost you in audit hours, and a realistic timeline for a pilot. The engineers come from regulated backgrounds, including ISO 27001 and pharma environments, so the scoping conversation moves fast because the assumptions are already right. If you’re evaluating whether to build or keep renting, see how Autonomousfirm builds AI-native firms and schedule a discovery call to map your first pilot.
Standards Worth Reviewing Before You Build
Before committing to a build, review the primary technical references that shape how automated controls get defined and validated. NIST’s cyber framework profiles provide the mapping baseline most automation systems build against. MITRE D3fend translates controls into concrete technical countermeasures, and MITRE SAF’s Vulcan tooling supports continuous validation of those controls in production.
Sources
- NIST cyber framework profiles
- OSCAL (NIST) machine-readable controls
- The Future of Compliance: Shift to Proactive Security | CSA
- FINOS common cloud controls project
FAQ
How Can AI Be Used in Compliance?
AI extracts obligations from regulatory text, scores risk across systems, and continuously checks production environments against defined controls. It replaces periodic manual review with ongoing evidence collection, which is the shift the Cloud Security Alliance describes as the move from reactive to proactive compliance.
How Do You Automate Compliance Processes?
Start by inventorying which systems and frameworks matter most, then pilot policy-as-code checks wired into your CI/CD pipeline for one framework before expanding. This approach is phased, moving from a single pilot system to full-scale monitoring over several quarters.
How Can AI Be Used for Automation Generally?
Beyond compliance, AI automates pattern recognition, document classification, and repetitive validation tasks across finance, healthcare, and operations workflows. In compliance specifically, the highest-value automation targets are obligation extraction and evidence collection, since both consume the most manual hours today.
Will Compliance Officers Be Replaced by AI?
No. Automated systems handle extraction, monitoring, and evidence gathering, but human reviewers still confirm high-stakes findings, interpret ambiguous regulatory language, and own escalation decisions. The realistic model is expert-in-the-loop, where compliance officers shift from manual evidence-gathering toward judgment calls the system flags for them.
What Does It Cost to Build an AI-Native Compliance System?
Pricing depends on scope, systems involved, and frameworks targeted, so current figures are listed directly on the Autonomousfirm site rather than as a fixed number here. A discovery call typically scopes cost against your specific pilot before any commitment.